
ISO 42001 AI Governance Consultancy
- Home
- ISO 42001 AI Governance Consultancy
Put responsible AI governance into practice
Understand where AI is used, who is accountable, and how risks are managed. CyberTech Labs helps organizations plan and implement an AI management system aligned with ISO/IEC 42001:2023, with a practical roadmap from initial assessment to ongoing review.
Discuss your AI governance needs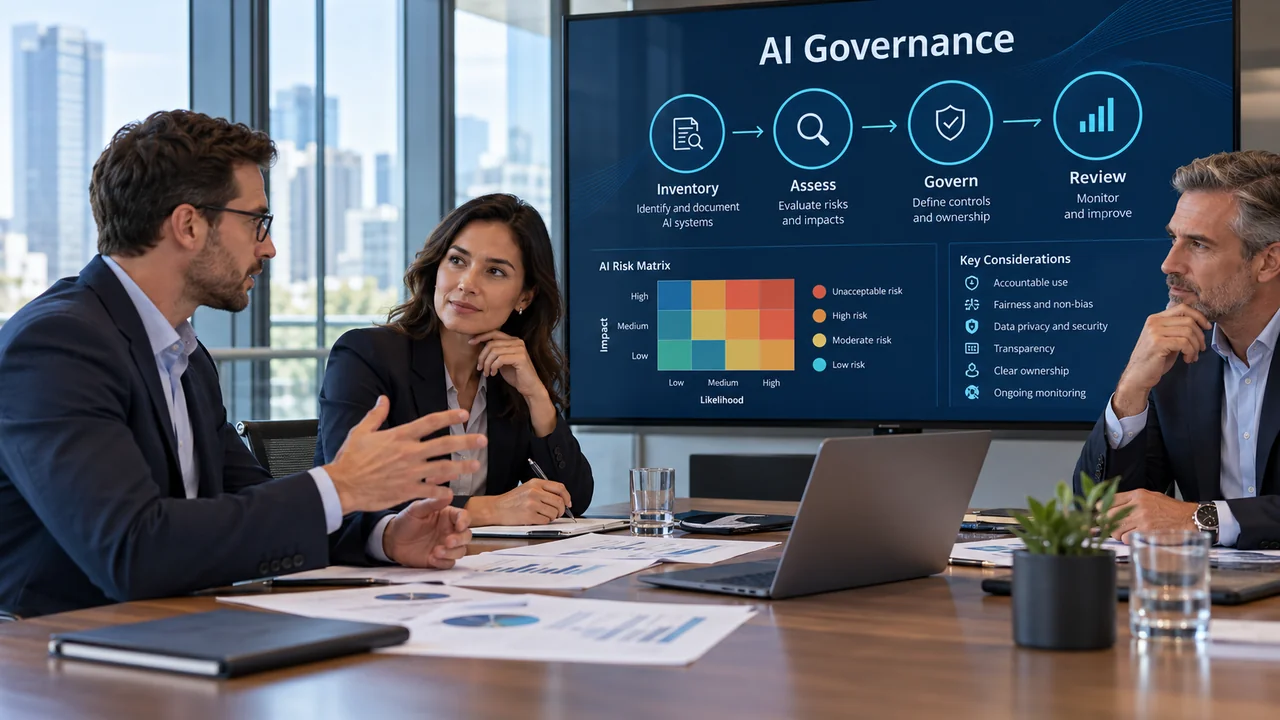
Who this service is for
Organizations developing, supplying, or using AI need a consistent way to make decisions about it. This engagement can support teams introducing AI-enabled products, adopting third-party AI tools, or responding to customer questions about responsible AI use.
We start with your actual use cases and business objectives, then agree on the boundaries of the management system and the work needed to support it.
What the engagement can cover
- Readiness assessment: review current governance arrangements, identify gaps, and prioritize the next steps.
- AI inventory and ownership: document relevant systems, intended uses, accountable roles, and third-party dependencies.
- Risk and impact assessment: establish a repeatable process to evaluate AI-related risks, potential impacts, and treatment actions.
- Policies and operating processes: support AI policies, oversight responsibilities, supplier reviews, and lifecycle documentation.
- Evidence and review: organize records, define monitoring measures, and support internal review and corrective-action planning.
A clear route from assessment to implementation
- Define the scope. Identify stakeholders, AI use cases, business drivers, and the parts of the organization in scope.
- Assess the starting point. Review existing processes and agree on a prioritized gap assessment.
- Build the management system. Develop the agreed policies, responsibilities, assessment methods, and records with your team.
- Review and improve. Evaluate implementation evidence, address open actions, and prepare for the next internal or external review.
The agreed scope determines the deliverables, schedule, and responsibilities. Your team remains involved so the resulting processes can be maintained after the engagement.
Build on your existing information security program
If you already operate an information security management system, we can review where governance activities overlap and where AI needs separate treatment. ISO 27001 consultancy and ISO 42001 support address related but distinct management objectives; one does not automatically satisfy the other.
For organizations building AI-enabled software, governance decisions should also inform requirements, implementation, and ongoing maintenance. Explore our software development service to discuss the technical side of your project.
ISO 42001 consultancy: common questions
What does ISO/IEC 42001 cover?
It sets requirements for an organizational AI management system: the policies, responsibilities, and processes used to manage AI-related risks and opportunities and improve them over time. It is not a certificate for the accuracy or safety of an individual AI model.
Can an organization that uses third-party AI work toward ISO 42001?
Yes. The standard applies to organizations that use AI as well as those that develop or provide it. The scope and applicable responsibilities need to reflect how the organization uses those systems.
Does consultancy include issuing a certificate?
No. Our role is assessment, implementation support, and readiness preparation. Certification decisions are made by an independent certification body following its audit process.
What do we need for an initial discussion?
A summary of your AI use cases, the teams involved, existing governance or security policies, and any customer or certification objectives. We can use those inputs to define a suitable engagement.
About the standard: ISO/IEC 42001:2023 — AI management systems.